How to Become a SOC Analyst: A Step-by-Step Career Roadmap
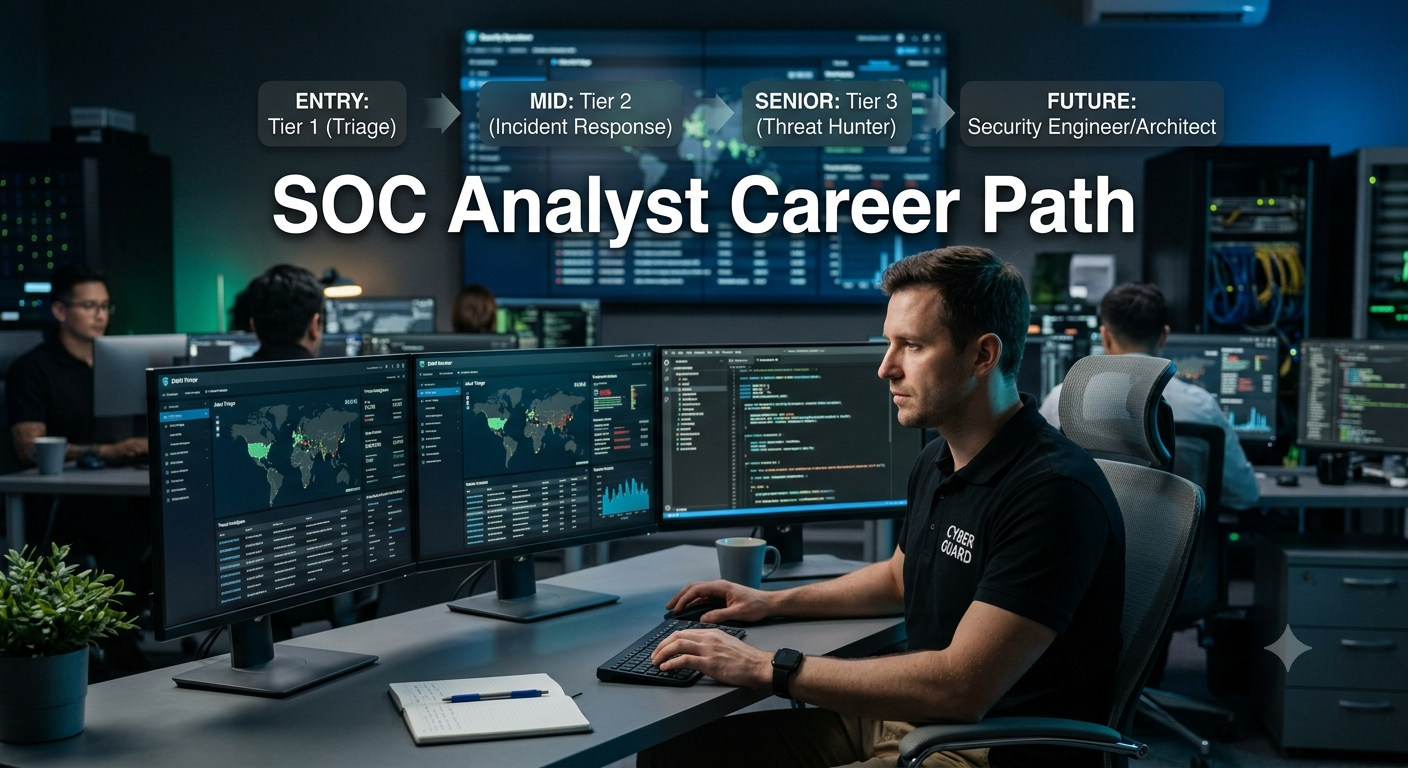
Want to start a career in cybersecurity? Learn how to become a Security Operations Center (SOC) Analyst, even if you are starting with limited security experience. This practical guide covers the skills to learn first, certifications to consider, SIEM tools to practise, home lab projects to build, and how to prepare for entry-level SOC jobs.
What Does a SOC Analyst Do?
A Security Operations Center Analyst monitors an organization's systems, networks, and security alerts to identify suspicious activity. SOC analysts investigate potential threats, examine logs, determine whether an alert is legitimate, document their findings, and escalate confirmed or complex incidents to the appropriate team.
A SOC is part of an organization's defensive security operation. Its purpose is to detect, investigate, and support responses to threats such as compromised accounts, malware infections, phishing attacks, suspicious network connections, and unauthorized access.
What does a SOC Analyst actually investigate?
Imagine a monitoring tool detects multiple failed logins followed by a successful login from an unusual location. A SOC analyst checks the account activity, timestamps, source IP address, related authentication events, and any other available evidence to determine whether the activity is suspicious.
Common SOC Analyst responsibilities
- Alert triage: Review alerts, establish their severity, and decide which require further investigation.
- Log analysis: Examine Windows, Linux, firewall, authentication, and application logs.
- Threat investigation: Correlate events to understand what happened and identify possible indicators of compromise.
- Incident escalation: Share evidence and findings with incident responders or senior analysts when necessary.
- Documentation: Maintain investigation notes, incident tickets, and shift handover records.
SOC work is not simply running commands or watching a dashboard. The most important skills are understanding the evidence, asking the right questions, and explaining why an event should or should not be treated as a threat.
SOC Analyst Tiers Explained
Many security operations teams divide responsibilities into tiers. The exact structure varies between employers, and some smaller SOCs use different job titles or combine several responsibilities into one position.
| Role | Main Responsibilities | Typical Focus |
|---|---|---|
| Tier 1 Analyst | Monitor alerts, perform initial triage, collect evidence, and escalate incidents. | Detection and triage |
| Tier 2 Analyst | Conduct deeper investigations, correlate events, and support incident handling. | Investigation |
| Tier 3 Analyst | Perform advanced analysis, threat hunting, detection engineering, or complex incident investigations. | Advanced detection and response |
Tier 1 is a common entry point into a traditional SOC, although junior security analyst and security monitoring roles may have similar responsibilities without using a tier designation.
Progression depends on practical skills, investigation experience, organizational needs, and available opportunities rather than a fixed number of years.
Essential Skills for a SOC Analyst
You do not need to master every cybersecurity technology before applying for an entry-level position. Start with the fundamentals that help you understand alerts and investigate suspicious activity.
1. Networking Fundamentals
Learn how devices communicate and how normal traffic behaves. Focus on TCP/IP, DNS, HTTP and HTTPS, common ports, routing, subnetting, NAT, and firewall rules. These concepts help you understand network alerts and identify unusual connections.
2. Windows and Linux
Understand users, processes, permissions, services, authentication, and system logs. Windows Event Logs and Linux authentication and system logs can provide important evidence during investigations.
3. Log Analysis and SIEM
A Security Information and Event Management (SIEM) platform collects and correlates security events from different sources. Learn how to search logs, filter events, investigate timestamps, and correlate related activity across multiple systems.
4. Security Concepts
Understand phishing, malware, brute-force attacks, privilege escalation, credential theft, indicators of compromise, vulnerabilities, and incident response. You should also know the difference between a security alert, a suspicious event, and a confirmed incident.
5. Analytical Thinking and Communication
Good analysts do not jump to conclusions based on one event. They gather evidence, test possible explanations, record uncertainty, and communicate their conclusions clearly to teammates and stakeholders.
6. Basic Scripting
Basic Python or PowerShell can help you parse data, automate repetitive tasks, and investigate events. Start by understanding scripts and making small modifications rather than trying to automate everything.
SOC Analyst Roadmap for Beginners
Follow this learning path to build a foundation for entry-level SOC applications. The time required depends on your previous IT experience, study schedule, and opportunities for practical work.
Learn Networking and Operating Systems
Start with TCP/IP, DNS, common ports, firewalls, Windows Event Logs, and Linux system logs. Practise explaining what happens when a device connects to a website or when a user authenticates to a system.
Helpful practice: use Wireshark to examine network packets and understand how protocols communicate.
Learn Security Monitoring and Alert Triage
Understand how monitoring tools collect security events, generate alerts, and help analysts investigate suspicious behavior. Practise reading event details and identifying what evidence is missing before making a decision.
Learn the basic incident response process: preparation, detection and analysis, containment, eradication, recovery, and lessons learned.
Practise Searching and Investigating Logs
Choose one platform to start with, such as Splunk, Microsoft Sentinel, Elastic Security, or Wazuh. Learn how to search events, filter results, examine time ranges, and correlate related activity.
Begin with authentication events, suspicious processes, unusual network connections, and repeated failed login attempts. Learn one platform well before trying to learn several at once.
Complete Blue Team Labs
Use authorized training environments to practise phishing analysis, authentication investigations, malware alert triage, and network traffic analysis. Platforms such as TryHackMe and Hack The Box offer structured cybersecurity learning opportunities.
Focus on explaining the investigation process, not simply completing a challenge or collecting a certificate.
Document Your Investigations
Create clear reports that explain the scenario, evidence reviewed, investigation steps, findings, limitations, and recommended response. A small collection of well-documented projects can help demonstrate practical knowledge to recruiters.
Apply for Entry-Level Security Roles
Tailor your resume to each job description. Highlight relevant IT support, networking, troubleshooting, security monitoring, and lab experience. Prepare to explain how you would investigate common security alerts.
Search for SOC Analyst Tier 1, junior security analyst, security monitoring analyst, and other entry-level defensive security positions.
How long does this roadmap take?
There is no universal timeline. Someone with existing networking and IT support experience may progress faster than a complete beginner. Measure progress by your ability to investigate logs, explain security events, use a SIEM, and present practical work—not just the number of courses completed.
Best Certifications for Aspiring SOC Analysts
Certifications can help structure your learning and demonstrate foundational knowledge. Their value depends on the employer, job description, your experience, and the practical skills you can demonstrate.
| Certification | What It Helps You Learn | When to Consider It |
|---|---|---|
| CompTIA Security+ | Core security concepts, threats, risk, and security operations. | Foundational security learning |
| CompTIA Network+ | Networking concepts that support troubleshooting and traffic analysis. | When networking knowledge needs work |
| Blue Team Level 1 (BTL1) | Practical defensive security skills and investigation exercises. | When seeking hands-on blue team practice |
| CompTIA CySA+ | Security analytics, vulnerability management, and incident response. | After developing foundational skills |
| GIAC GCIH | Incident handling and attack investigation concepts. | When aligned with career goals and budget |
You do not need to earn every certification on this list. Review current job postings in your target market and choose credentials that match the requirements you repeatedly encounter.
A certification is most useful when you can explain its concepts and apply them in practical investigations. Avoid delaying applications indefinitely while pursuing additional credentials.
Tools SOC Analysts Should Learn
SOC analysts use different tools depending on their employer, environment, and responsibilities. Beginners should focus on understanding what each tool does and how it contributes to an investigation.
| Tool Category | Examples | Purpose |
|---|---|---|
| SIEM | Splunk, Microsoft Sentinel | Search, correlate, and investigate security logs. |
| Endpoint Detection and Response | Microsoft Defender for Endpoint and other EDR platforms | Investigate suspicious endpoint behavior. |
| Network Analysis | Wireshark | Inspect packets and investigate network activity. |
| Network Discovery | Nmap | Understand hosts, ports, and services in authorized environments. |
| Log Analysis | Windows Event Viewer, Linux system logs | Examine authentication, system, and application events. |
| Case Management | Ticketing and incident management platforms | Document investigations, ownership, and escalation. |
Which tool should you learn first?
Start with Windows and Linux logs, then choose a SIEM that you can practise with consistently. Add Wireshark to understand network traffic. Learn other tools when they support a specific investigation or appear in the job descriptions you are targeting.
You can explore our Wireshark guide and Kali Linux guide to develop practical technical skills. Kali Linux is useful for security labs, but learning defensive monitoring and log analysis is particularly important for SOC-focused preparation.
Practical SOC Analyst Projects for Your Resume
Practical projects give you an opportunity to demonstrate how you think through a security problem. Start with small, clearly documented investigations rather than attempting to build a large enterprise security lab.
Project 1: Investigate Failed Login Attempts
Examine sample or lab-generated authentication logs and investigate repeated failed logins followed by a successful login.
- Identify relevant timestamps and account activity.
- Compare source IP addresses and event sequences.
- Explain which additional evidence you would need.
- Write a short investigation report with your findings.
Project 2: Analyze Suspicious Network Traffic
Use Wireshark to inspect traffic from an authorized lab or a suitable sample capture. Identify protocols, endpoints, unusual connections, and patterns that deserve further investigation.
- Document the capture source and investigation scope.
- Identify relevant IP addresses and protocols.
- Explain why specific traffic appears noteworthy.
- Include screenshots with sensitive information removed.
Project 3: Create a Basic SIEM Investigation
Use an available SIEM lab to search a dataset, investigate an alert, and correlate related events. Describe how you would decide whether to escalate.
- Explain the alert and the potential risk.
- Record the search logic and relevant event fields.
- Summarize evidence supporting your conclusion.
- Recommend appropriate next investigative steps.
How to present projects professionally
For each project, include the objective, environment, tools used, methodology, evidence, findings, and limitations. Clearly label simulated findings as lab results. Never publish confidential employer data, real credentials, or private security logs.
How to Get Your First SOC Analyst Job
Getting your first security role is easier to approach when you can demonstrate both foundational knowledge and the ability to investigate practical scenarios. There is no guaranteed combination of certifications and projects that results in a job offer, but the following steps can strengthen your applications.
1. Build a Relevant Resume
Highlight networking, troubleshooting, log analysis, ticketing, documentation, and security lab experience. If you have worked in IT support, explain how you investigated technical issues, handled escalations, and followed established procedures.
2. Demonstrate Practical Skills
Include a small number of relevant projects that you can explain confidently. Be ready to discuss the evidence you examined, how you reached a conclusion, and what you would investigate next.
3. Prepare for Technical Interviews
Practise explaining DNS, TCP and UDP, common ports, authentication logs, phishing indicators, SIEM searches, false positives, and incident escalation. Interviewers may ask you to reason through a scenario rather than simply define a technical term.
4. Apply for Related Entry-Level Roles
Search for SOC Analyst Tier 1, junior security analyst, security operations, monitoring analyst, and suitable IT support roles with security responsibilities. Adjacent positions can provide experience that supports a future move into a SOC.
5. Match Your Applications to Real Job Descriptions
Identify recurring requirements in your target market. If employers frequently ask for a particular SIEM, Windows logging, or cloud security knowledge, prioritize those skills rather than studying every tool available.
Entry-level SOC application checklist
- Understand networking and operating system basics.
- Know how to investigate common security alerts.
- Practise searching logs in at least one SIEM.
- Prepare practical projects you can discuss in interviews.
- Tailor your resume to each relevant position.
- Keep improving through feedback and additional practice.
What Does a SOC Analyst Do Every Day?
A typical SOC workday may involve reviewing alerts, investigating unusual events, updating incident tickets, and communicating with teammates. The precise routine depends on the organization's size, security tools, threat environment, and analyst responsibilities.
Alert Review and Triage
Analysts review new alerts, assess their severity, and determine whether the available evidence justifies additional investigation. Some alerts are benign or false positives; others require escalation.
Investigation and Documentation
When an alert deserves attention, analysts examine relevant logs, user activity, endpoint information, and network events. They document the evidence, findings, and recommended next steps.
Escalation and Team Handover
More complex incidents may require incident responders, senior analysts, or other security teams. SOC teams also maintain case notes and handover information so investigations can continue across shifts.
Are SOC Analysts Required to Work Night Shifts?
Some SOCs operate around the clock and use rotating shifts, including nights, weekends, and holidays. Others follow regular business hours. Check each employer's shift requirements before accepting a role.
SOC Analyst Career Progression
SOC experience can lead to several areas of cybersecurity. The best direction depends on the work you enjoy, the skills you develop, and the opportunities available in your organization.
| Career Direction | Main Focus |
|---|---|
| Incident Responder | Investigates confirmed incidents and supports containment, eradication, and recovery. |
| Threat Hunter | Proactively searches for hidden or previously undetected threats. |
| Detection Engineer | Develops, tests, and improves detection rules and security monitoring logic. |
| Security Engineer | Designs, implements, and maintains security technologies and controls. |
| Penetration Tester | Performs authorized security testing to identify and validate vulnerabilities. |
| Cloud Security Specialist | Focuses on cloud identity, configuration, monitoring, and security controls. |
You do not need to decide on a specialization before entering cybersecurity. Build strong fundamentals, gain investigation experience, and use that experience to identify which area best fits your interests.
Frequently Asked Questions About Becoming a SOC Analyst
Do I need a degree to become a SOC Analyst?
Not every SOC position requires a university degree. Employers may consider a combination of education, certifications, practical skills, and relevant IT experience. However, some organizations have specific degree requirements or use them as part of their recruitment screening.
How long does it take to become a SOC Analyst?
The timeline varies with your starting knowledge, available study time, and hands-on practice. People with networking or IT support experience may already have useful foundations. Focus on demonstrating job-relevant skills rather than relying on a fixed preparation timeline.
Is CompTIA Security+ enough to get a SOC job?
Security+ can demonstrate foundational security knowledge, but it does not guarantee employment. Combine certification study with SIEM practice, log analysis, relevant projects, and interview preparation. Check the requirements of employers in your target market.
Which SIEM should a beginner learn first?
Splunk, Microsoft Sentinel, Elastic Security, and Wazuh are possible starting points. Choose one based on your learning resources and target job descriptions. Learn to search, filter, correlate, and interpret events before moving to another platform.
How can I gain SOC experience without a security job?
Practise with authorized blue team labs, SIEM training environments, sample log datasets, and network captures. Document your investigation process and findings in a portfolio. Clearly distinguish lab experience from professional employment on your resume.
What projects should I include on a SOC Analyst resume?
Useful examples include authentication log investigations, phishing email analysis, SIEM alert triage, and network traffic analysis. Choose projects that demonstrate your reasoning, evidence collection, documentation, and understanding of appropriate response actions.
Can I become a SOC Analyst with no IT experience?
Yes, it is possible, although some entry-level positions may be competitive. Start with networking, operating systems, security fundamentals, and practical labs. Consider IT support or junior technical roles as alternative ways to gain relevant troubleshooting experience.
Is SOC Analyst work stressful?
It can be, particularly during active incidents, high alert volumes, or demanding shifts. Analysts need to prioritize effectively, document decisions, and follow escalation procedures. Workload and stress vary by employer, team structure, and role.
What is the difference between a SOC Analyst and a Penetration Tester?
SOC analysts primarily monitor, investigate, and respond to potential security threats. Penetration testers perform authorized testing to discover security weaknesses. Both roles require technical knowledge, but their objectives and daily workflows are different.
Do SOC Analysts need to know Python?
Advanced programming is not a universal requirement for entry-level SOC roles. Basic Python can help with parsing logs, processing data, and automating repetitive tasks. Prioritize networking, operating systems, SIEM searches, and investigation fundamentals before moving to more advanced automation.
Final Thoughts: Start Your SOC Analyst Journey
Becoming a SOC Analyst is about more than collecting certifications or learning a long list of tools. You need to understand how systems work, recognize suspicious behavior, investigate evidence, and explain your findings clearly.
Start with networking and operating system fundamentals. Learn how to examine logs, practise with a SIEM, and complete authorized defensive security labs. Document your work, prepare for technical interviews, and apply for roles that match your current skills while continuing to learn.
You do not have to know everything before taking your first step. A focused learning plan, practical experience, and consistent improvement can help you work toward an entry-level cybersecurity role.